

Website Hacking Techniques: Real Attack Methodologies

What Does Website Hacking Really Mean? Website hacking is the process of finding and testing weaknesses in a website or web application. Ethical hackers perform these tests with permission to identify vulnerabilities before real attackers can exploit…
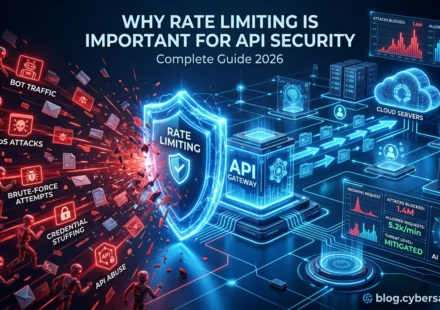
Why Rate Limiting is Critical for API Security
In 2022, a security researcher discovered that a popular social media platform’s password reset endpoint had no request limits. Using a simple script, they submitted 1,000 guesses against a six-digit OTP in under four minutes. The platform’s…
DOM-Based XSS
DOM-Based XSS: The Client-Side Threat Understanding and defending against the stealthiest XSS variant ⚠️ Ethical Note: This guide is for educational purposes only. Only test systems you own or have permission to test. What is DOM-Based XSS? DOM-Based…
CSRF Attacks: Bypassing SameSite Cookies
CSRF Attacks: Bypassing SameSite Cookies A comprehensive guide to understanding and exploiting CSRF vulnerabilities with SameSite bypass techniques ⚠️ Ethical Disclaimer: This guide is for educational purposes only. Only test systems you own or have…
Path Traversal Explained
Path Traversal: Escaping the Web Root Understanding and exploiting directory traversal vulnerabilities ⚠️ Ethical Disclaimer: This guide is for educational purposes only. Only test systems you own or have explicit permission to test. What is Path…
Remote Code Execution (RCE) Vulnerabilities Explained
Remote Code Execution (RCE) Vulnerabilities Explained The complete guide to understanding, finding, and preventing RCE flaws ⚠️ Legal Disclaimer: This guide is for educational purposes only. Unauthorized testing is illegal. What is Remote Code Execution?…